Passive Recon 2.0: Mapping Attack Surfaces While You Browse
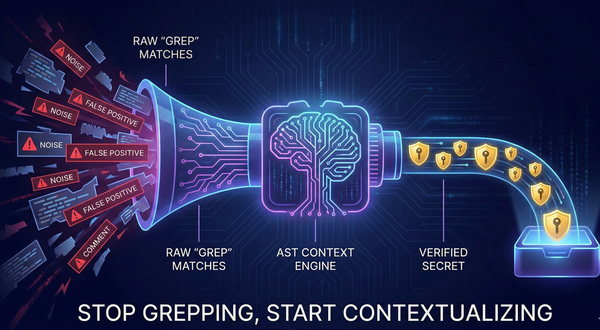
If you've ever done security reconnaissance on a web application, you know the drill. You spend time clicking around, understanding how the app works, mentally mapping out its functionality. Then you switch gears, fire up your terminal, run tools like waybackurls or subjs, download files, and start grepping