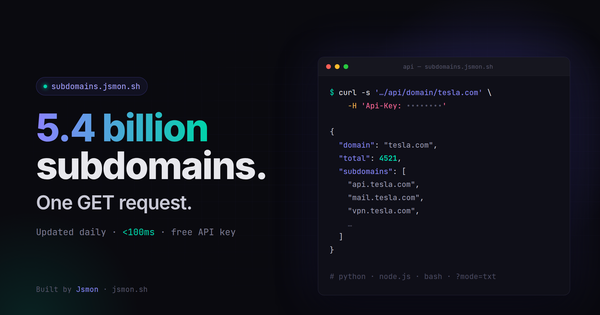
Query 5.4 Billion Subdomains with One API Call
Subdomains by Jsmon puts 5.4 billion subdomains behind a single GET request. Here's what's in the database, how the API works, and how to build a client in Bash, Python or Node.js in a few lines
Subdomains by Jsmon puts 5.4 billion subdomains behind a single GET request. Here's what's in the database, how the API works, and how to build a client in Bash, Python or Node.js in a few lines
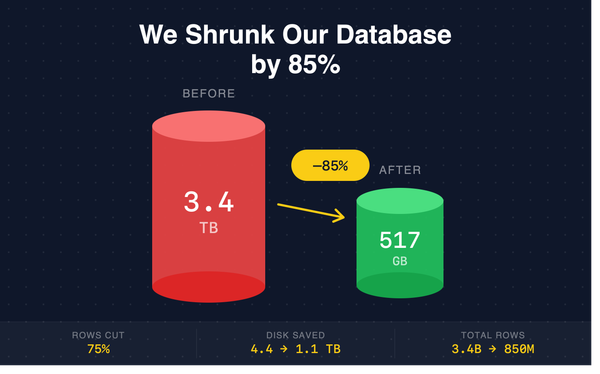
Migrating and Shrinking Jsmon's PostgreSQL DB from 3.4 TB to 517 GB. At Jsmon, our Application Exposure Intelligence platform scans millions of domains and processes billions of JavaScript intelligence signals
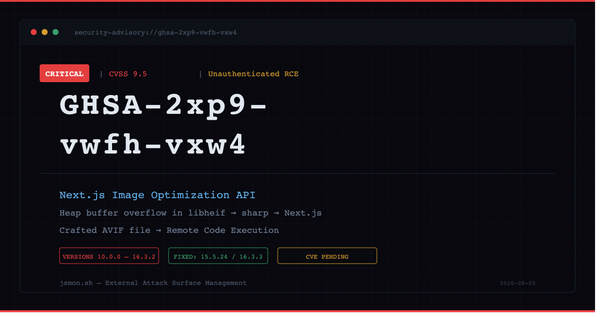
Critical heap buffer overflow in libheif chains through sharp into Next.js Image Optimization, enabling unauthenticated RCE via crafted AVIF files. Full analysis and remediation.
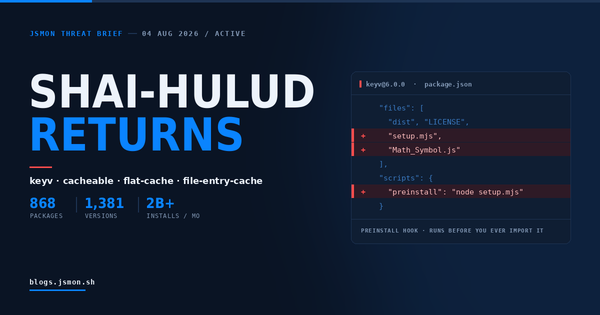
A compromised maintainer account pushed a preinstall dropper into keyv, cacheable, flat-cache and file-entry-cache on August 4, 2026. The payload fetches its own Bun runtime, drains cloud and CI credentials, and republishes itself through npm trusted publishing.
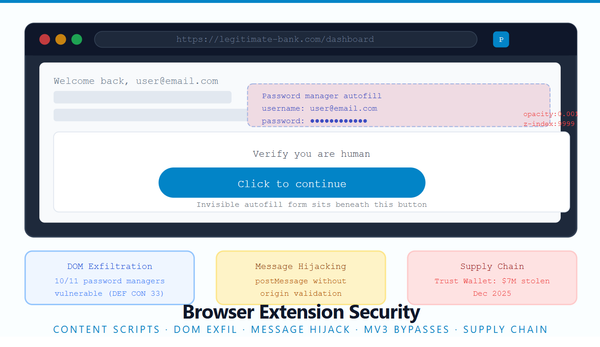
Browser extensions occupy a uniquely dangerous position in the security landscape. They are installed by users who trust them, they run inside the browser with elevated privileges, and they can touch every page you visit. More importantly, the security research community has largely ignored them in favour of server-side bugs,
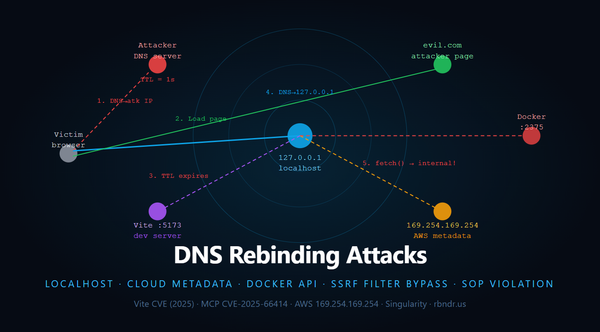
There's a mental model most developers carry around about localhost: it's safe because it's not accessible from the internet. The firewall doesn't touch it. External traffic can't reach it. Whatever's running on 127.0.0.1:3000, your
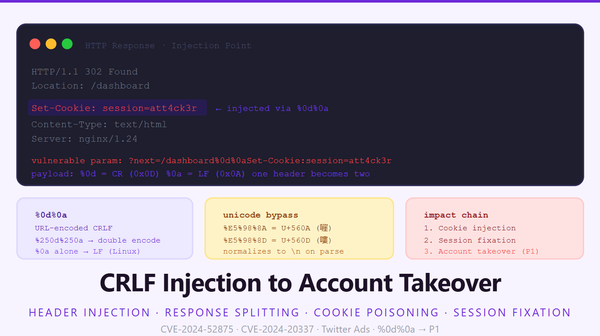
There's a category of bugs that always surprises people when they learn the payout. CRLF injection sounds boring, "oh you injected a newline", until you realize that a newline in an HTTP header means you can write entirely new headers, inject session cookies, force the browser
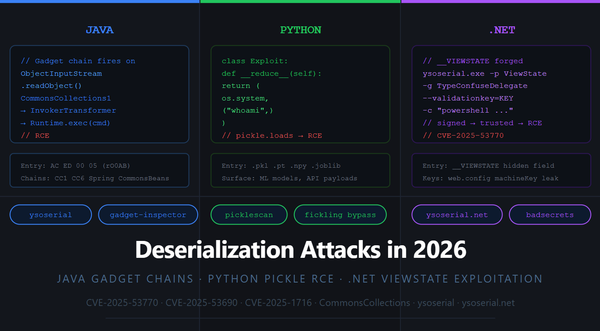
Deserialization vulnerabilities have been around since 2015 when Chris Frohoff and Gabriel Lawrence dropped their AppSecCali talk "Marshalling Pickles." More than a decade later, the class is still producing critical RCEs, not because nobody knows about it, but because it is genuinely hard to fix without breaking application
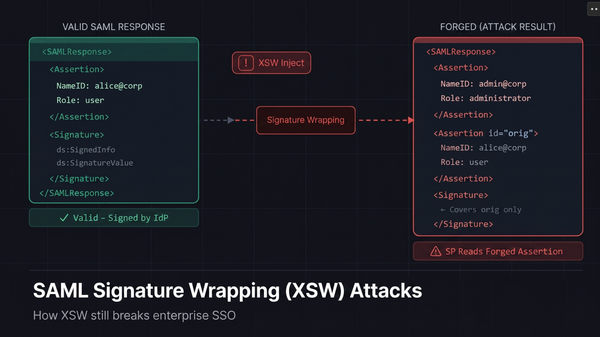
Here's something that'll mess with your head a little. When you log into Okta, Azure AD, Salesforce, or literally any enterprise app with SSO, there's a moment where a chunk of XML gets passed from the identity provider back to the application, and that
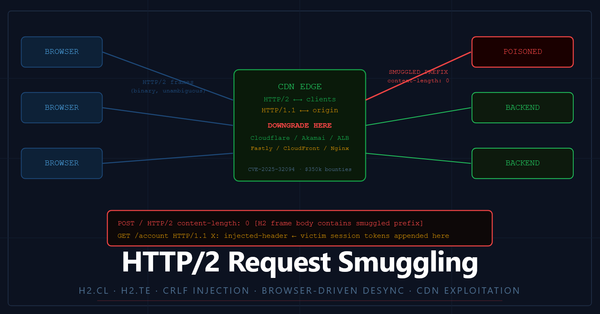
A lot of people still picture it as a 2019-era party trick: tweak Content-Length, maybe sneak in a weird Transfer-Encoding, and hope a proxy somewhere gets confused. Sometimes it works, often it doesn’t, and the whole thing can feel like chasing ghosts. In 2025 alone, James Kettle's

OAuth 2.0 and OpenID Connect (OIDC) are so common now that they fade into the background. “Sign in with Google,” enterprise SSO, partner integrations, mobile apps requesting API access, underneath, it’s almost always OAuth. That ubiquity has a side effect: OAuth bugs keep appearing in real production systems,
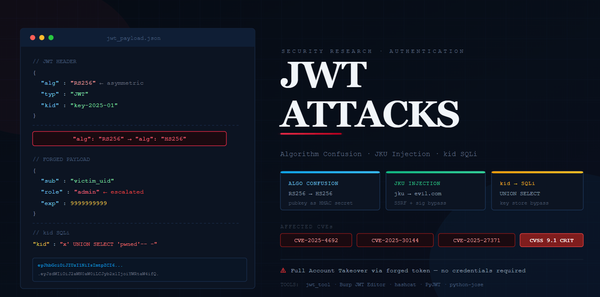
JSON Web Tokens (JWTs) are the de facto authentication primitive across modern web applications, microservices, and APIs. Yet their flexibility, specifically the delegated algorithm selection embedded within each token, has repeatedly proven catastrophic. Six new critical CVEs affecting widely-deployed JWT libraries were disclosed in 2025 alone, with several enabling full